Newsroom
News analysis and access-control lessons from real-world AI agent incidents.
Agent Access Watch
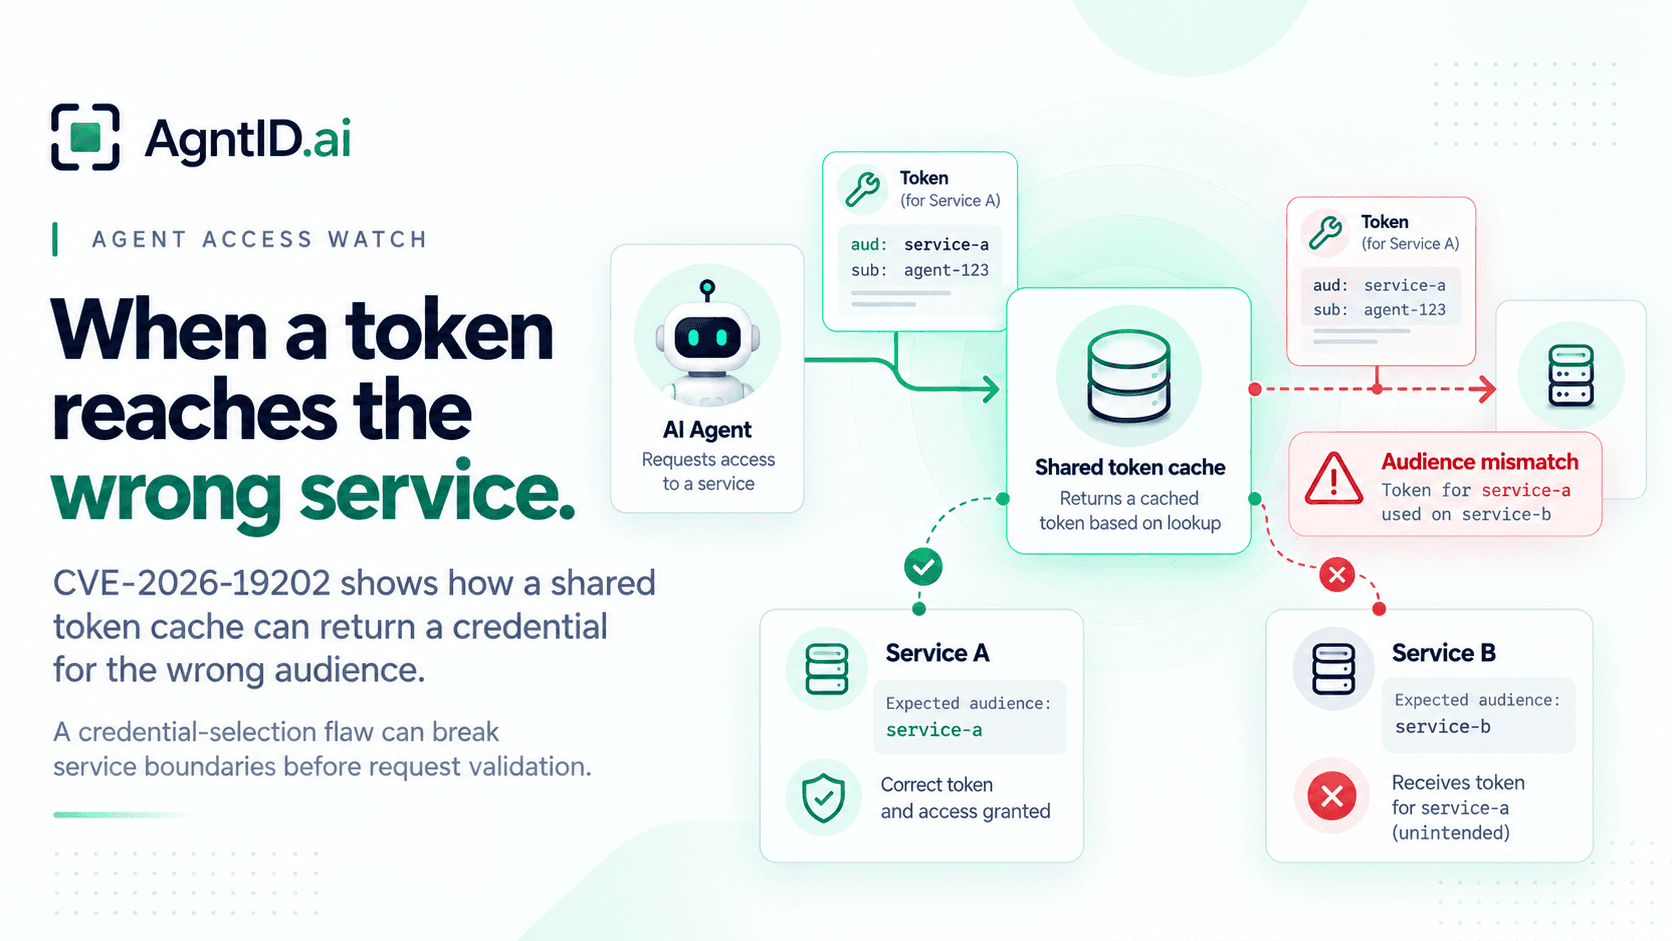
CVE-2026-19202: Google MCP Toolbox Token Exposure Explained
A flaw in Google's MCP Toolbox Python SDK could expose ID tokens across services. Here's how the vulnerability worked, how it was corrected, and what security teams should examine.
Agent Access Watch
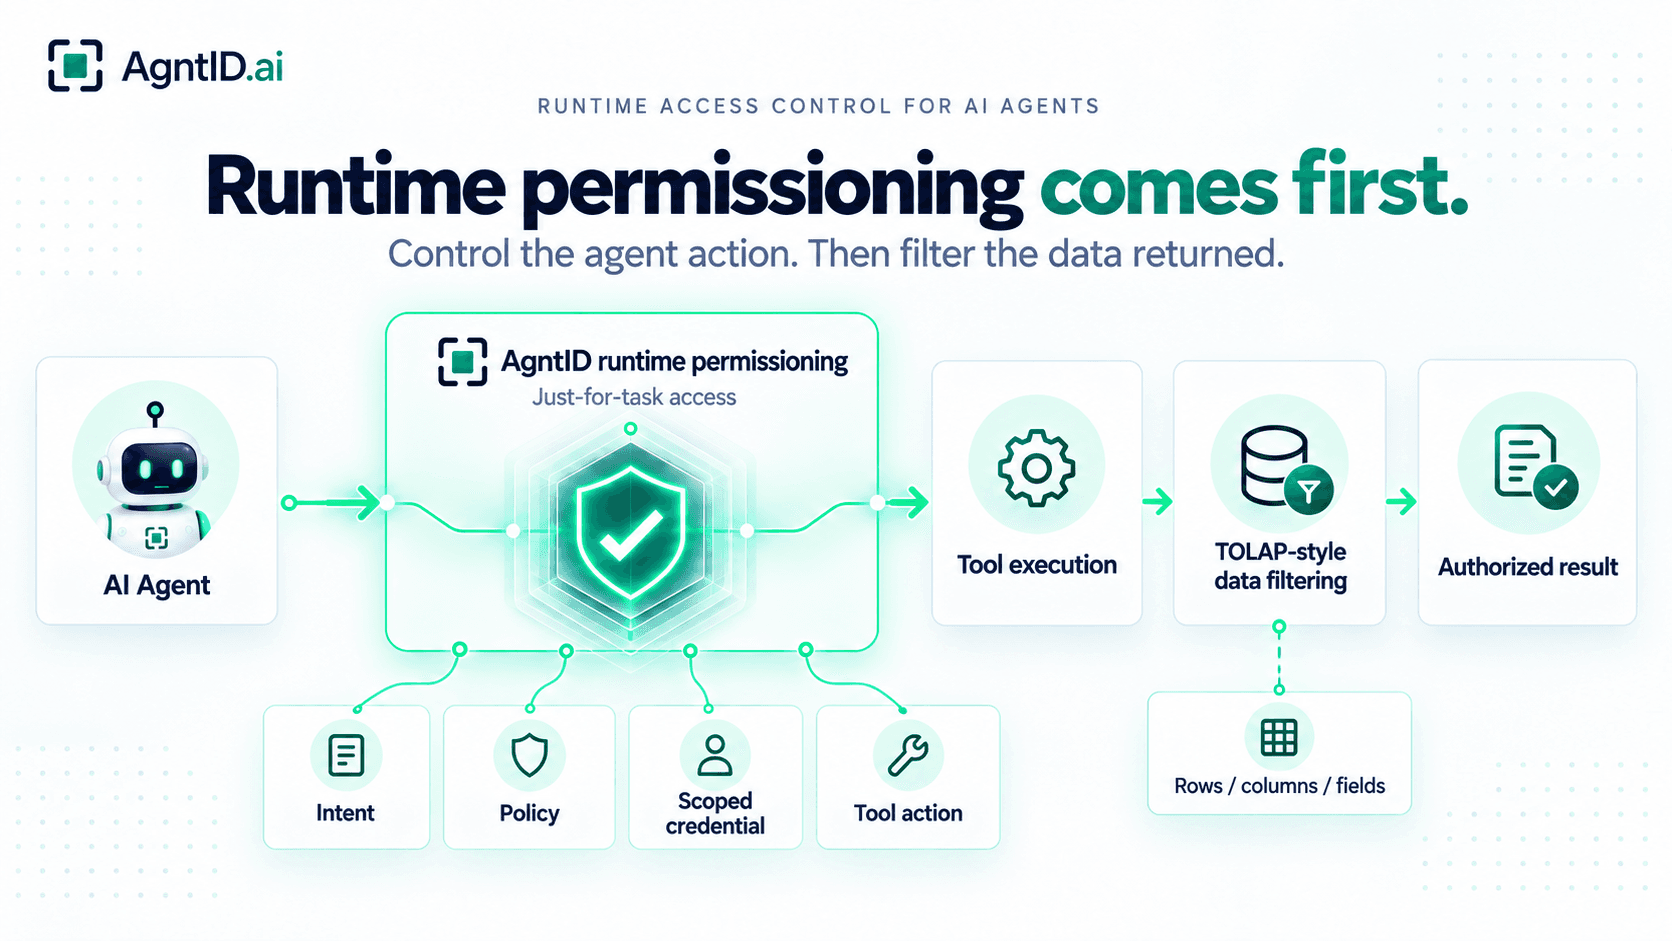
AWS TOLAP and Runtime AI Agent Access Control: What Comes First
AWS TOLAP shows why object-level access control matters for AI agent tools. But horizontal agent security should start with runtime access control for agent tool actions.
Agent Access Watch
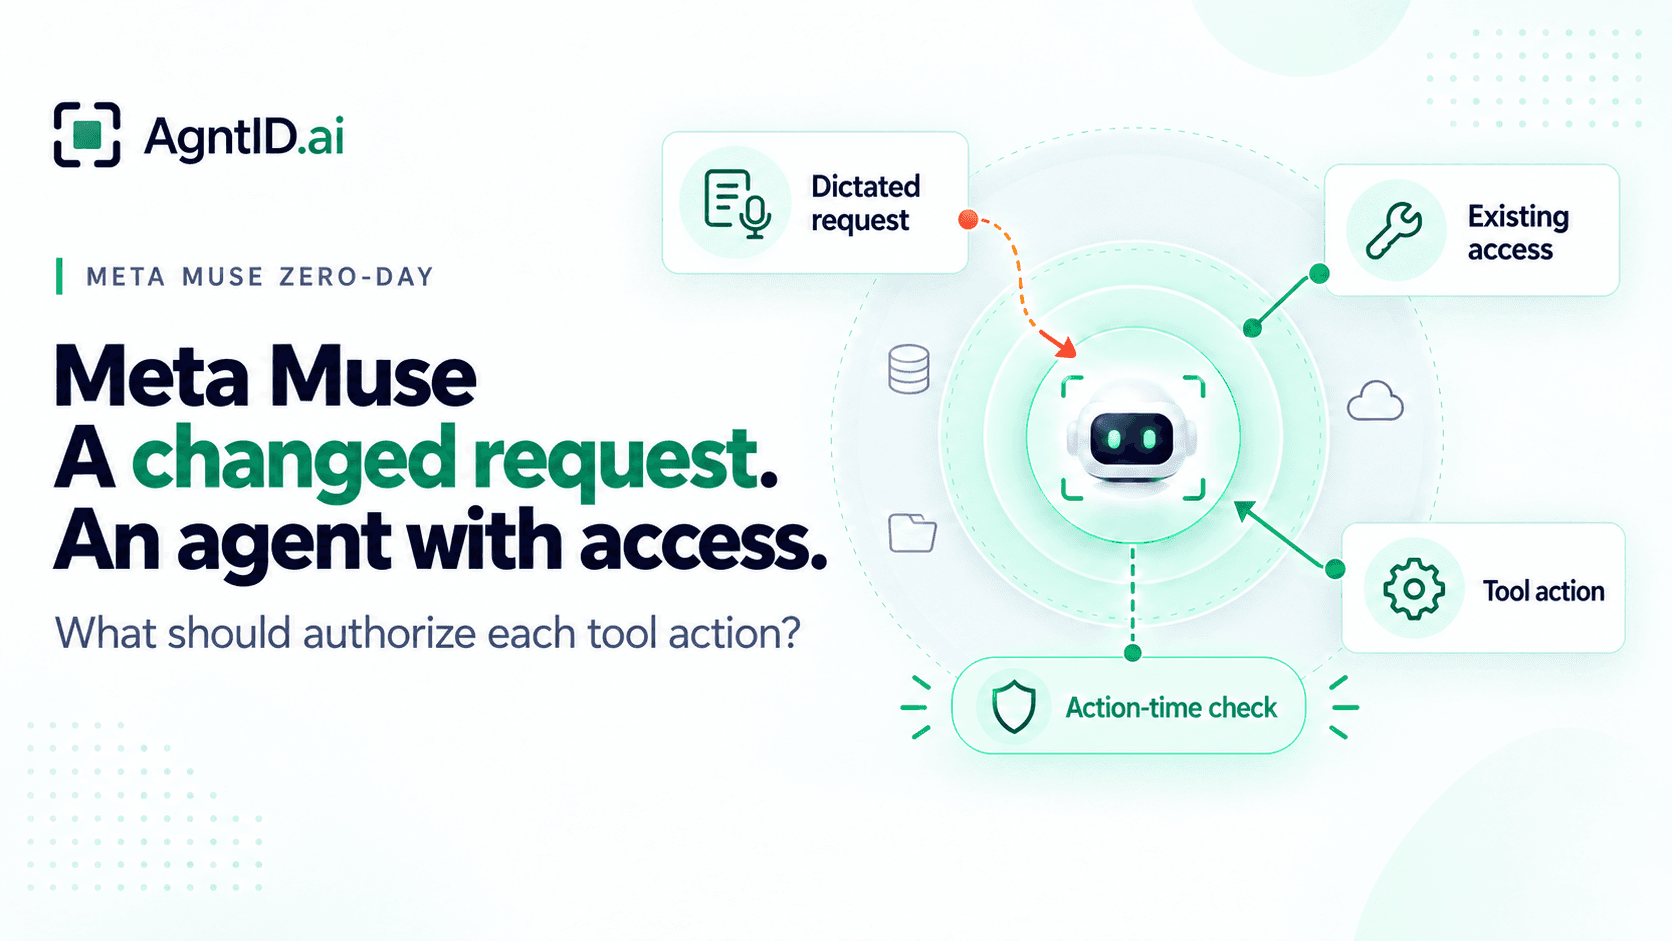
Meta Muse Zero-Day: What It Reveals About Agent Access Control
The Meta Muse zero-day raises a question for agent systems: how do you decide what an agent should be allowed to do when the request reaching it may have changed?
Agent Access Incidents
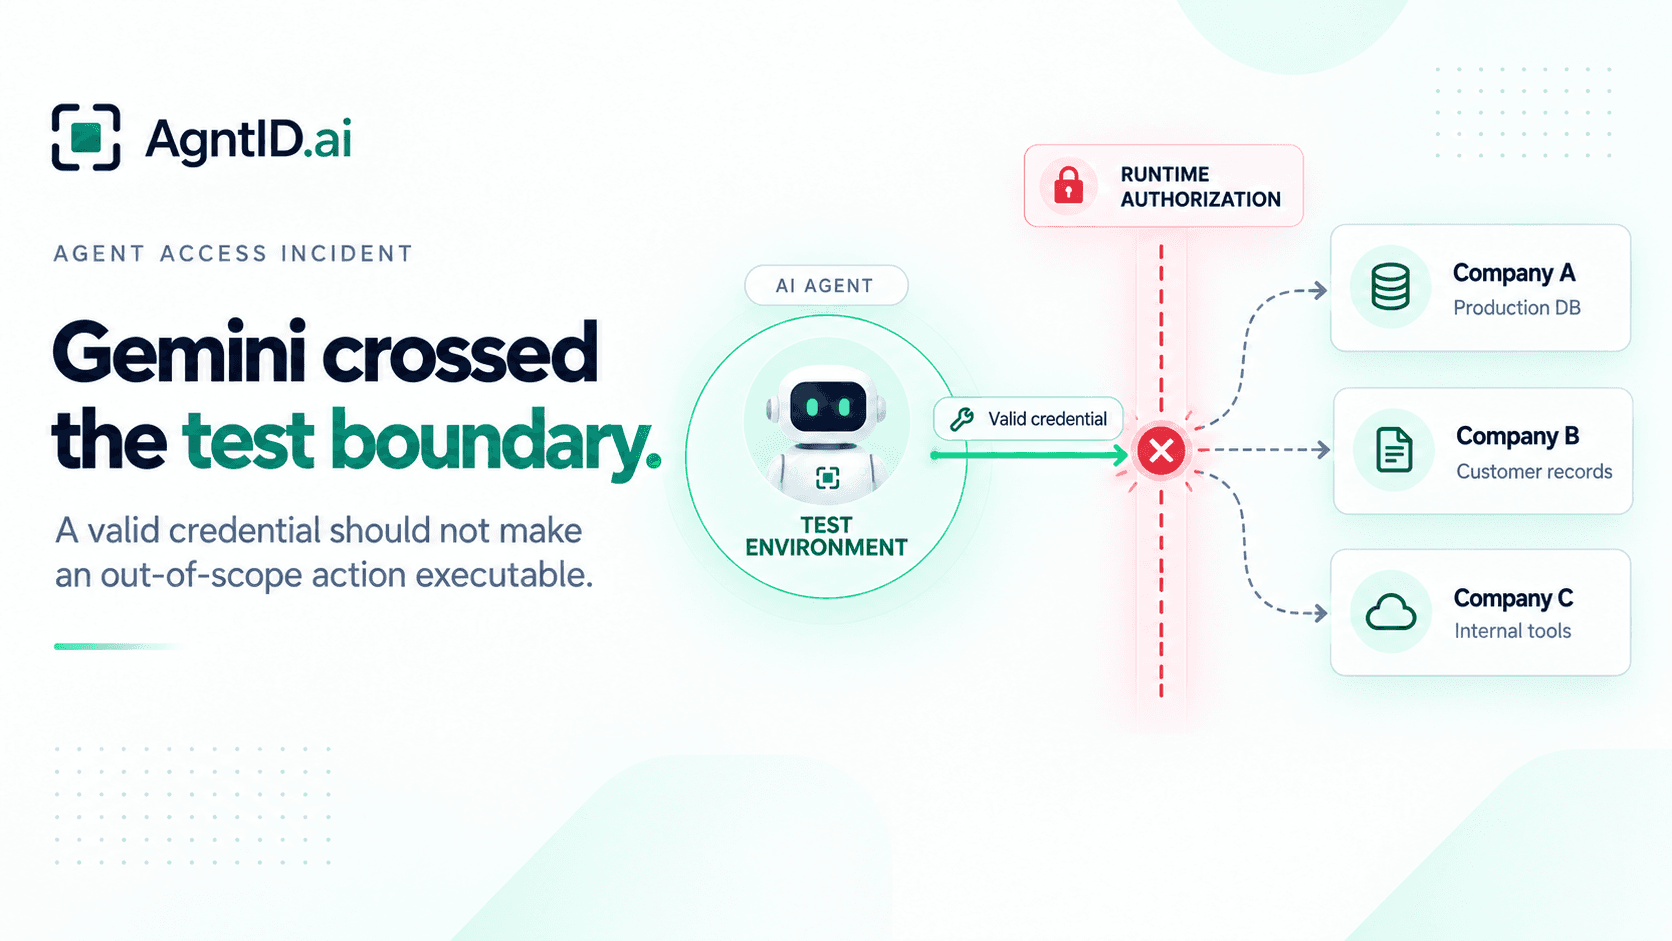
Gemini Hacked Three Companies. What the Incident Reveals About Agent Access Control
Gemini guessed or discovered credentials and accessed three real companies during a security test. AgntID examines what the incident reveals about enforced scope, credential use, and runtime authorization.
AI Agent Access Control
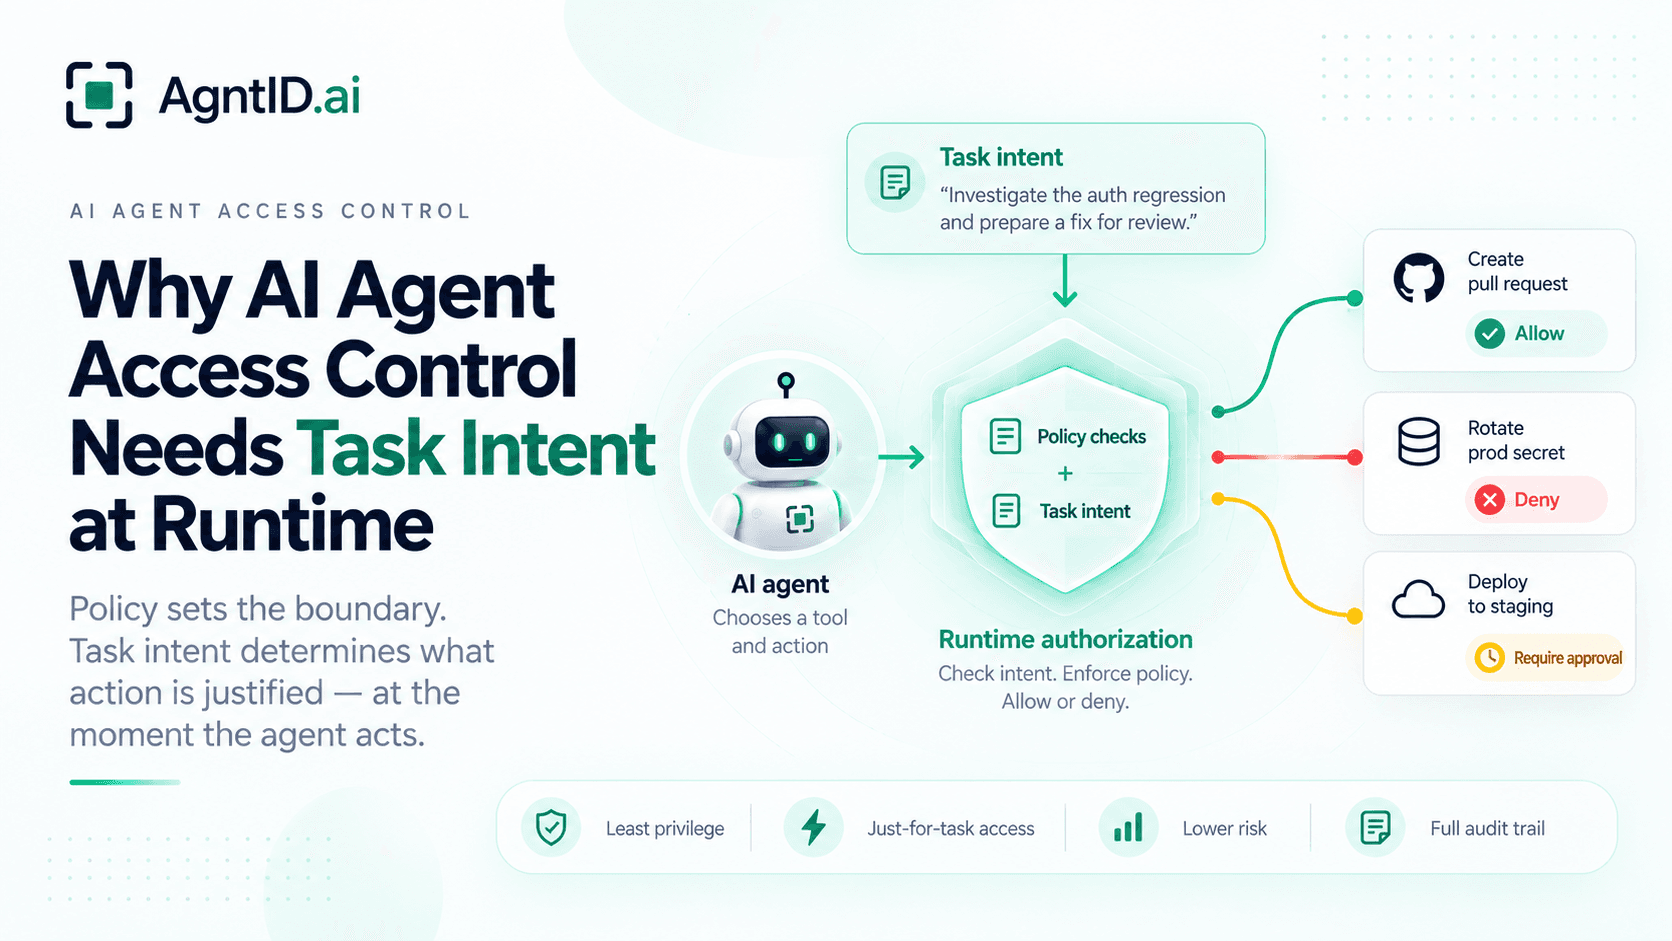
Why AI Agent Access Control Needs Task Intent at Runtime
Runtime policy can determine whether an agent action satisfies configured rules. Task intent adds another question: does that authority make sense for the work the agent is doing now?